Arcium
Arcium is a decentralized, parallelized confidential computing network that supports encrypted computations for AI and blockchain applications, founded in 2022 by Yannik Schrade, Julian Deschler, Nicolas Schapeler, and Lukas Steiner.[46] It describes itself as an “encrypted supercomputer” that provides a trustless, verifiable framework for running multi-party computation (MPC) over encrypted data across a distributed set of nodes, originating on Solana where encrypted computation is live on mainnet via Arcium Mainnet Alpha, a permissioned production phase launched in February 2026.[44][45]
Overview
Arcium, founded in 2022 by Yannik Schrade, Julian Deschler, Nicolas Schapeler, and Lukas Steiner, aims to provide a decentralized confidential computing network. The team previously built Elusiv, a zero-knowledge transaction privacy protocol on the Solana blockchain, before expanding their focus to general-purpose encrypted computation.[46] Arcium describes the network as an “encrypted supercomputer” that offers a parallelized confidential computing layer for AI, finance, and other data-intensive applications.[44]
In May 2024, Arcium completed a $5.5 million strategic funding round led by Greenfield Capital, bringing its total funding to $9 million. Participants in the round included Coinbase, Heartcore Capital, Longhash VC, L2 Iterative Ventures, Staking Facilities, Smape Capital, Everstake, and angel investors such as Solana co‑founder Anatoly Yakovenko and Monad co‑founder Keone Han.[46][47] As part of its evolution beyond Elusiv, Arcium acquired the core team and privacy-related intellectual property of MPC company Inpher, integrating its technology and cryptographers into the network’s encrypted computation stack.[45][47]
Arcium’s early development progressed through two private testnets, which the team reports attracted more than 50,000 applications to participate.[47] In May 2025, the project transitioned to Public Testnet Phase 1, shipping the initial on-chain programs, running internal clusters, and hosting early applications such as a dark pool trading demo while stress-testing network performance and node stability.[45][48]
According to the roadmap, Public Testnet Phases 2 and 3 are planned to deliver a more fully featured network with third‑party node operation, enhanced preprocessing, batch processing, and broader application coverage, including the launch of the C‑SPL confidentiality standard on Solana devnet.[48] Arcium Mainnet Alpha, launched on Solana mainnet in February 2026, is described as a permissioned production phase operated by Arcium with an initial cluster of independent node operators, intended to validate performance and stability before broader decentralization and the planned $ARX token launch.[45] In its published roadmap, the project targeted a fully decentralized mainnet and token generation event (TGE) in the first quarter of 2026 as a subsequent milestone.[48]
The network is designed for secure data collaboration in sectors like blockchain, healthcare, and AI, using a distributed node architecture to perform MPC-based encrypted computations while maintaining data confidentiality.[1][2] Its framework on Solana handles tasks such as computation scheduling and compensation, and aims to offer flexible MPC configurations for applications such as AI model training, confidential DeFi, and privacy-preserving data analysis.[1][44] A planned $ARX network token is intended to support staking and delegation to MPC nodes, accrue usage-based fees from on
- and off-chain activity including C‑SPL transactions, and enable on-chain governance over protocol upgrades.[44][48] Ahead of this token generation event, Arcium has outlined Retroactive Token Grants (RTGs) as a contribution-based rewards model for early users and developers instead of a traditional airdrop.[48][45]
Architecture
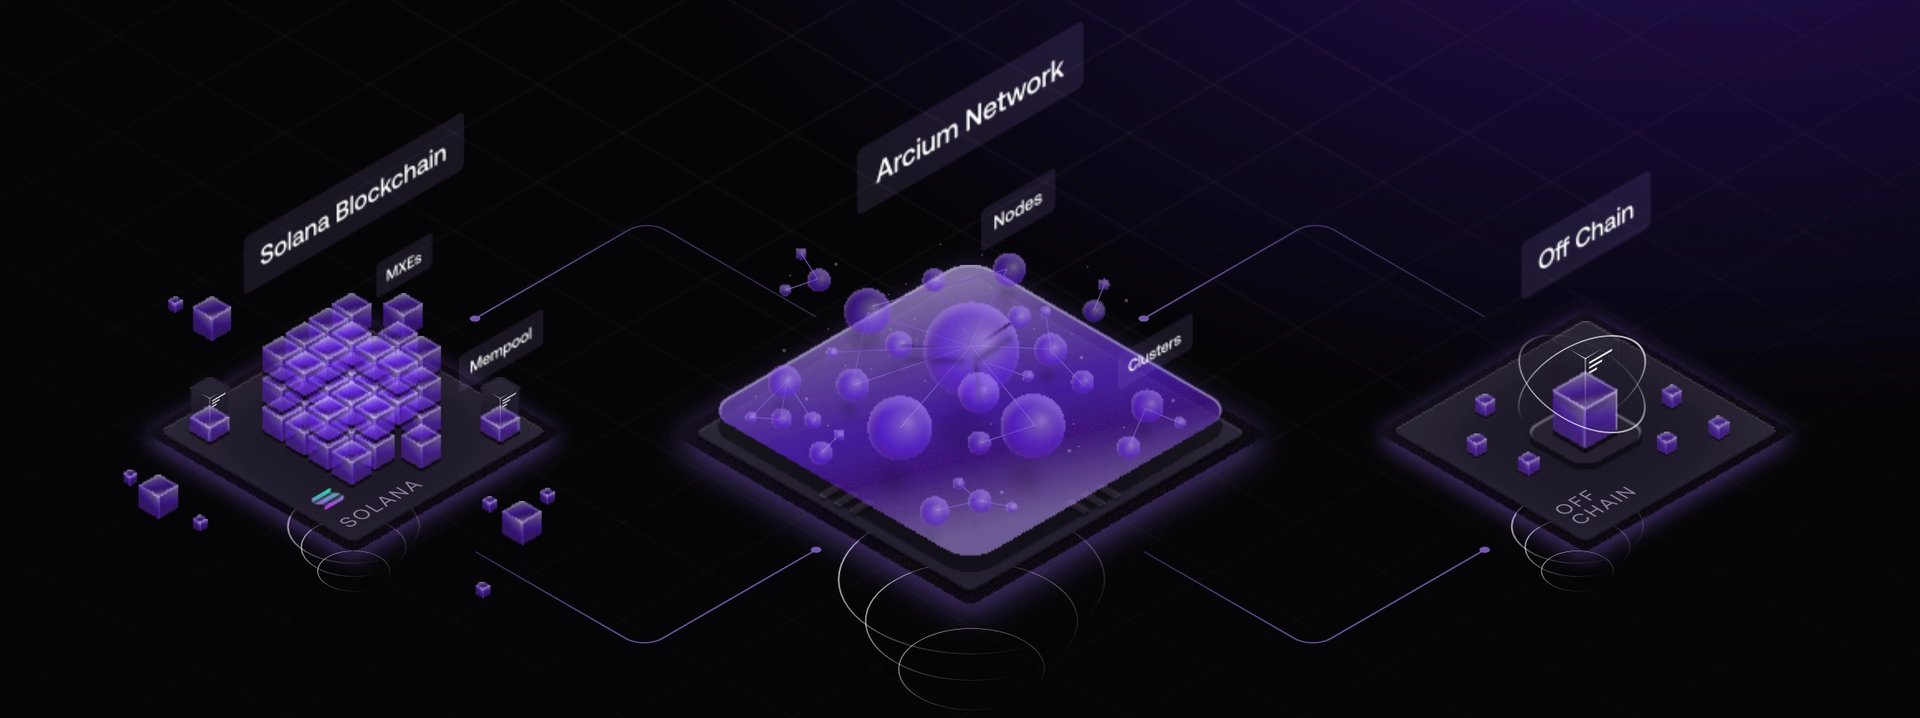
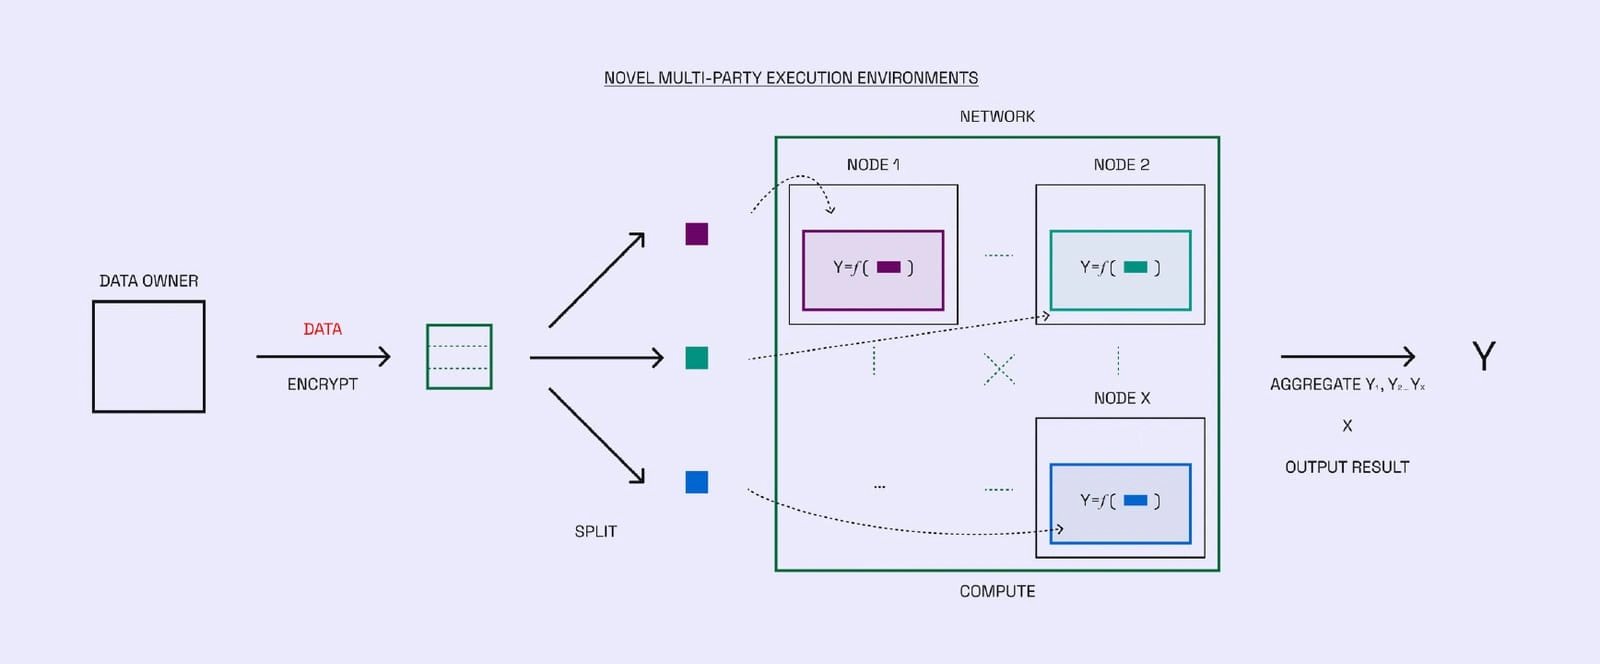
Arcium’s architecture is designed to support distributed confidential computing. It breaks tasks into computation definitions, which are executed in Multi-Party Computation (MPC) environments (MXEs) on clusters of Arx nodes, functioning like hardware for secure processing.
The network is coordinated by programs running on the Solana blockchain, aiming to manage tasks through an on-chain mempool system. Compensation for computational services is handled on-chain, facilitating payments from customers to Arx operators and third-party delegators.[4]
Products
Multi-Party Execution Environments (MXEs)
Multiparty Execution Environments (MXEs) aim to facilitate secure computations on encrypted data, enabling collaboration among multiple parties without revealing their inputs or outputs. Developers can customize the encryption schema based on the sensitivity of the data, generating a shared key for participating nodes.
MXEs serve as fundamental components of the Arcium Network and can be classified as Single Use, which execute one computation before being discarded, or Persistent, allowing for reuse. Clusters of nodes confirm their capacity to process tasks, perform necessary preprocessing, and retrieve inputs from the blockchain for concurrent processing. The network supports various MPC protocols, including BDOZ, to enhance efficiency and security.[3][5][6][7][8][9][10]
Clusters
Clusters are designed as groups of Arx nodes that aim to utilize multiparty computation (MPC) for confidential operations. Customers can form Clusters based on various node properties, including reputation and computational capacity.
During the creation of a Cluster, customers specify parameters such as maximum load and the number of Trusted Execution Environment (TEE)-enabled nodes. Most properties are fixed, with the exception of potential increases in load.
Nodes must provide consent to join a Cluster. In non-permissioned Clusters, a randomly selected node is added, and activation requires approval from all nodes. A Node Priority List is maintained for backup nodes.
Clusters manage cryptographic key operations through Distributed Key Generation (DKG) and can employ TEEs for enhanced confidentiality. Cluster forking enables remaining nodes to conduct separate computations if an MXE is ejected.
Migration costs are shared among nodes, and intentions to shut down must be communicated to prevent penalties. Rewards are allocated based on stake delegation, with a Leader node collecting output shares for additional compensation. Permissioned Clusters enable organizations to oversee their node infrastructure.[11][12][13][14][15][16][17][18][19][20]
Arx Node
Arx nodes function as fundamental components of the Arcium Network, aiming to facilitate distributed computing for complex tasks. Each node retains a single encrypted data fragment, employing the Multiparty Computation (MPC) protocol to enhance data privacy.
Nodes are associated with Node Operators, who may manage multiple nodes. Relevant metadata includes the node's IP, port, and jurisdiction codes. Arx nodes also manage key shares securely and may utilize Trusted Execution Environments (TEEs) to strengthen security.
Node Operators generate income through self-delegation and fees from third-party delegations. Reputation is evaluated based on historical performance, with the network currently supporting the BDOZ MPC protocol and plans for future protocol expansions.
Middlelayer Nodes aim to connect off-chain data to computations, requiring a degree of trust from users. Reliable infrastructure is essential for node operation, and the support of TEEs may increase potential revenue opportunities.[3][21][22][23][24][25][26][27][28][29][30]
Computations
The Arcium Network differentiates between system and normal computations. System computations are designed to support network operations, including DKGSystemComputation for distributed key generation, MigrationSystemComputation for cluster migrations, and NonParticipationDetectionSystemComputation, which aims to trigger broader consensus when non-participation is detected.
Normal computations refer to customer-initiated tasks associated with an MXE, defined in Computation Definitions that specify outputs and execution authority levels. The execution logic utilizes public or private circuits based on the BDOZ protocol for efficient cryptographic operations. Customers are responsible for setting parameters for data sources while maintaining data integrity and confidentiality. A deterministic pricing model facilitates cost pre-assessment and allows for priority enhancements through additional fees, with node operators voting to establish sustainable pricing.[31][32][33][34][35][36][37][38]
Decentralized Confidential Computing (DeCC)
Decentralized Confidential Computing (DeCC) aims to ensure secure processing of sensitive data without exposure. It combines decentralization, which distributes data across multiple locations, with confidentiality measures to protect against unauthorized access. This approach addresses growing concerns over data privacy while facilitating secure processing in the Web3 ecosystem.
DeCC utilizes technologies such as Multi-Party Computation (MPC), Zero-Knowledge Proofs (ZKPs), Fully Homomorphic Encryption (FHE), and Trusted Execution Environments (TEEs) to maintain data privacy during processing. The Arcium framework applies these DeCC principles to create a structure for encrypted computations, aiming to reduce the risk of data breaches by preventing any single entity from having full access to complete datasets.[43]
Cerberus
Cerberus is Arcium’s main cryptographic backend for secure multiparty computation (MPC), designed for zero‑trust environments. It operates in the dishonest‑majority security model, remaining secure even if all but one of the participating parties are corrupted, and provides identifiable abort to pinpoint and exclude misbehaving parties.[49]
The protocol composes low‑level primitives such as oblivious transfer (OT), oblivious linear evaluation and its vector form VOLE, authenticated secret sharing, and signatures into an input‑independent preprocessing phase followed by an online phase that evaluates arbitrary arithmetic circuits with low communication overhead.[49] Cerberus is designed to run over a decentralized substrate that offers public, append‑only communication and accountability, using a blockchain to anchor state, input and output delivery, and economic incentives so that mutually distrustful nodes can perform outsourced computation while remaining accountable.[49]
Use Cases
Arcium's confidential computing network aims to enhance data security and privacy across various sectors. Key use cases include:
- AI: Aims to facilitate the secure pooling of encrypted data for collaborative AI training while preserving the privacy of individual datasets.
- Decentralized Finance (DeFi): Aims to encrypt DeFi actions and expand into Real-World Assets (RWAs) to promote compliance and protect user data.
- Decentralized Physical Infrastructure Networks (DePIN): Aims to ensure secure handling of sensitive data in decentralized services without exposing the data.
- Healthcare: Aims to enable secure collaboration on sensitive patient data, facilitating analysis for personalized medicine while preserving privacy.[3][42]
Ecosystem
Solana Integration
Arcium utilizes Solana, an open-source blockchain that facilitates decentralized applications and transactions. On-chain programs on Solana are responsible for managing the Arcium Network, which includes the registration of Arx nodes, computation processing, and financial activities such as payments and rewards.[39]
The network implements a dual-mempool structure: the active mempool for computations ready for execution and the dependent mempool for computations awaiting the completion of others. This design aims to improve organization by directing computations to clusters of Arx nodes.[40] Arcium is also developing C‑SPL (Confidential SPL‑Token), a confidentiality standard for Solana that combines existing token infrastructure with Arcium’s encrypted compute to enable confidential DeFi and payments; C‑SPL is planned to launch on Solana devnet as part of Public Testnet Phase 2.[48] Usage‑based fees from on‑ and off‑chain interactions with Arcium, including C‑SPL transactions, are intended to accrue to the planned $ARX network token, alongside its roles in staking, delegation to MPC nodes, and on‑chain governance.[44]
While the integration is initially with Solana, Arcium aims to support multiple blockchains and off-chain environments as the network matures.[3][41]